

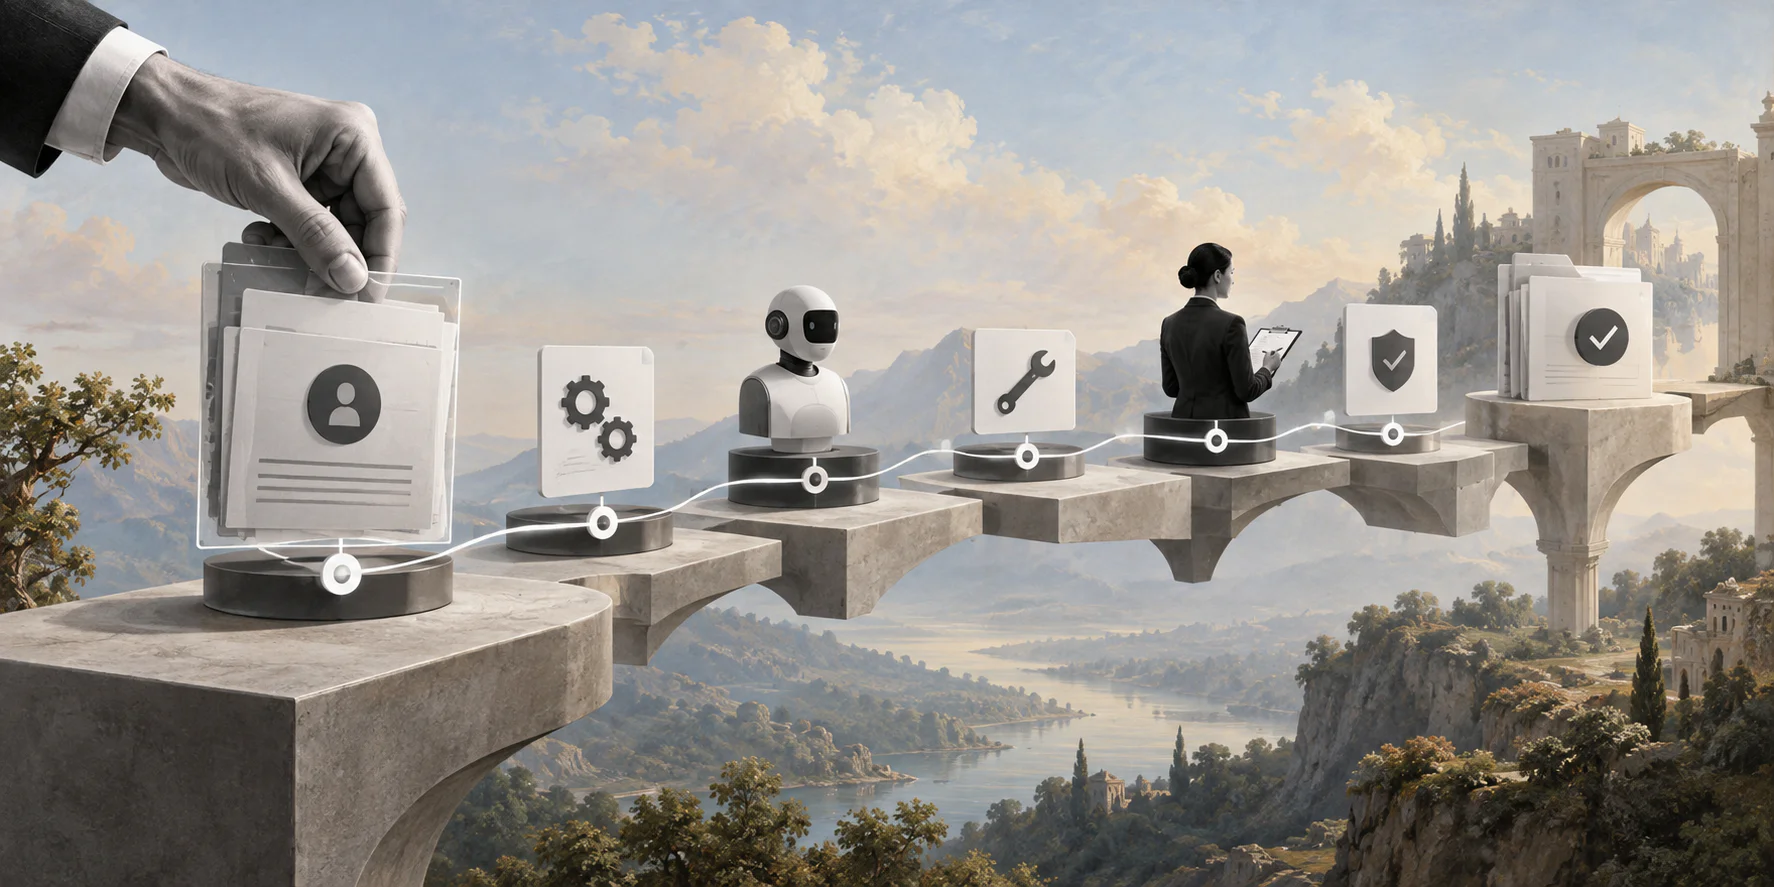
AI agents do not become trustworthy because they act faster; they become trustworthy when every action can be reconstructed.
AI agent audit trails are the structured records that show what an AI agent saw, decided, requested, approved, changed, and escalated. They matter when agents move beyond drafting text and begin using tools, updating systems, routing work, preparing payments, sending messages, or recommending approvals.
Quick answer
An AI agent audit trail should capture the request, user or agent identity, data sources, model and prompt version, tool calls, policy checks, human approvals, system changes, errors, and final outcome. The goal is not to store every raw prompt forever. The goal is to create enough evidence for operations, security, compliance, and finance teams to reconstruct what happened and why.
What are AI agent audit trails?
AI agent audit trails are evidence records for agentic workflows. A normal application log might show that an API call succeeded. An agent audit trail has to show the chain of work: the trigger, sources retrieved, model output, tools called, approval decision, and downstream result.
This is becoming a practical business requirement. The NIST AI Risk Management Framework organizes AI risk around governance, mapping, measurement, and management. For agentic workflows, those ideas become operational records: who owned the workflow, what risk was mapped, what was measured, and what control handled the outcome.
Why audit trails matter for AI workflow automation
AI workflow automation introduces a different kind of risk from ordinary automation. A deterministic rule usually follows a fixed path. An AI agent may classify a request, retrieve context, choose a tool, draft a response, update a record, and decide whether the next step should continue or pause.
If the workflow works, that flexibility removes manual coordination. If it fails, the team needs more than a chat transcript. They need to know whether the wrong data was retrieved, the tool was over-permissioned, the approval gate was skipped, or the downstream system accepted a bad payload.
Microsoft’s guidance on least privilege for AI agents makes the same point from an access-control angle: agents should have dedicated identity, scoped permissions, controlled tool access, and auditability. Without that structure, teams cannot tell what the agent was allowed to do or contain the blast radius when something goes wrong.
What should an AI agent audit trail include?
A useful audit trail should be structured enough to query and specific enough to support review. Start with the event, then record each material decision and action.
| Audit area | What to capture | Why it matters |
|---|---|---|
| Identity | User, agent, service account, role, workflow owner | Shows who or what initiated the run |
| Input | Request ID, source system, document references, timestamps | Connects the workflow to the original business event |
| AI context | Model, prompt version, retrieval sources, output, confidence signal | Explains what shaped the recommendation |
| Tool activity | Tool called, arguments, response, errors, retry behavior | Shows how the agent interacted with business systems |
| Approval | Reviewer, decision, exact payload approved, timestamp, comments | Proves human oversight for consequential actions |
| Outcome | Record updated, message sent, task assigned, payment prepared, exception raised | Confirms what changed after the decision |
How to design audit trails for business workflows
Start with one workflow rather than a general logging program. An invoice exception agent needs different evidence from an HR case-routing agent or a customer support triage agent.
1. Define the business object
Every run should attach to a durable object: invoice, vendor request, work order, support case, candidate record, contract review, access request, or payment batch. Without that anchor, audit records become disconnected technical events.
2. Separate request, decision, and execution
Do not collapse the whole run into one log line. Record the request that started the workflow, the AI or rule-based decision that shaped the route, and the final execution result. This makes it easier to diagnose whether the issue came from bad input, weak reasoning, poor permissions, or a downstream failure.
3. Bind approvals to the exact action
An approval record should show what the reviewer saw and what action was approved. If the agent changes the amount, recipient, message, or target record after approval, the workflow should require a new approval. The AWS Agentic AI Lens recommends risk-tiered approval workflows, reviewer context, escalation paths, and logged approval decisions.
4. Log exceptions, not only success
Successful runs are not enough. Log missing data, permission denials, rejected approvals, failed tool calls, duplicate requests, timeouts, model errors, human overrides, and rollback actions. Exceptions are often where the real operating risk lives.
5. Protect sensitive data in the audit layer
Audit trails should not become a second warehouse of exposed personal, financial, or customer data. Store references, hashes, masked previews, and secured record links where possible. Give audit access only to people who need it, and define retention by risk level and regulatory context.
Example AI agent audit trail for invoice approvals
Consider a finance team using an AI agent to review invoice exceptions. The agent reads the invoice, checks the purchase order, identifies a price mismatch, and prepares an approval packet.
The audit trail should show the invoice ID, vendor ID, purchase order snapshot, model output, policy threshold, mismatch amount, reviewer, approval decision, final status, and any payment-preparation step. If the agent retries a failed ERP update, the retry should be visible and idempotent so the invoice is not posted twice.
For lower-risk work, such as summarizing an internal request, a lighter trail may be enough. For finance, HR, procurement, legal, security, or compliance-sensitive workflows, the trail should support a later investigation.
Where Workhint fits
Workhint fits at the workflow orchestration layer around the AI agent. The model may classify, extract, summarize, draft, or recommend. Workhint helps organizations turn that output into a configurable workflow automation software system with intake, roles, permissions, assignments, approvals, documents, schedules, payments, reporting, and automation rules.
For audit trails, that means the evidence stays connected to the work itself. A vendor review, invoice exception, contractor onboarding step, or customer request can carry its intake record, AI recommendation, reviewer decision, approval status, assignment history, and final outcome in one operating workflow.
Common mistakes
- Logging only the final answer: The answer does not show sources, tool calls, approvals, or system changes.
- Storing raw sensitive data everywhere: Audit records should preserve evidence without creating unnecessary privacy exposure.
- Using chat approval as the only record: Approval needs to be tied to the exact business object and action payload.
- Skipping versions: Teams need to know which rule, prompt, model, or workflow version was active at the time.
FAQ
What is an AI agent audit trail?
An AI agent audit trail is a structured record that shows the request, data sources, model output, tool calls, approvals, actions, exceptions, and final outcome of an AI-assisted workflow.
Do AI audit trails need full prompt transcripts?
Not always. High-risk workflows may need stronger records, but many teams can store structured outputs, source references, prompt versions, hashes, and approval evidence instead of retaining every raw prompt in full.
What is the difference between observability and auditability?
Observability helps teams debug performance, latency, errors, and system health. Auditability helps reviewers reconstruct what happened, who authorized it, what evidence existed, and whether the workflow followed policy.
Which AI workflows need the strongest audit trails?
Use stronger audit trails for workflows involving money, workers, customers, vendors, contracts, access, regulated data, external communications, policy exceptions, or irreversible system changes.
Conclusion
AI agent audit trails are not a compliance afterthought. If an agent can retrieve data, call tools, recommend action, or change records, the business needs evidence that explains the run from intake to outcome.
The strongest teams design audit trails before expanding autonomy. They define the business object, record sources and decisions, bind approvals to exact actions, capture exceptions, and protect sensitive data. That is how AI agents move from impressive demos to accountable business workflows.
Leave a Reply