

A segregation of duties matrix helps teams prevent one person from owning a whole risky workflow.
A segregation of duties matrix is a practical control table that shows which roles should request, approve, execute, record, and review sensitive work. It is useful when operations teams design approval workflows, access requests, vendor onboarding, payments, contract reviews, data changes, or any process where one unchecked role could create errors, fraud, policy gaps, or audit problems.
Quick answer
A segregation of duties matrix lists critical process steps, the roles involved, incompatible duty combinations, approval rules, compensating controls, and evidence requirements. To build one, start with high-risk workflows, separate requester, approver, executor, recorder, and reviewer duties, define conflicts, document exceptions, and turn the matrix into workflow rules, permissions, approvals, and review reports.
What’s in this article?
- What a segregation of duties matrix is
- Why it matters for operating workflows
- The fields to include in a practical SoD matrix
- A step-by-step setup process
- Common mistakes that weaken the control
What is a segregation of duties matrix?
A segregation of duties matrix, often shortened to SoD matrix, is a table that identifies which duties should not be performed by the same person or role inside a critical process. The basic control idea is simple: the person who initiates a sensitive action should usually not be the only person who approves it, executes it, records it, and reviews it.
This matters because many operating risks are not caused by one dramatic failure. They come from everyday workflows where too much authority sits in one place. A user can create a vendor and approve payment. A requester can approve their own purchase. An administrator can grant access and review their own access change. A manager can approve an exception without a second record. The matrix makes those conflicts visible before the workflow is automated.
The U.S. Government Accountability Office’s Green Book treats segregation of duties as a key control activity, and COSO’s internal control framework similarly emphasizes separating incompatible duties or using alternative controls when separation is not practical. For business operations, the lesson is direct: workflow design should include control design.
Why segregation of duties matters in workflows
Operations teams often focus on speed first. They want fewer approvals, faster routing, and less manual work. That is reasonable, but speed without duty separation can create hidden risk. The right question is not “How do we add more approvals?” The better question is “Which actions require independent authority or review?”
Segregation of duties is most useful when a workflow touches money, access, customer commitments, vendor records, employee data, compliance evidence, legal obligations, or production systems. The matrix helps process owners decide where a control belongs and where it would only slow down routine work.
For example, a vendor onboarding workflow may need one role to request the vendor, another to verify payment details, another to approve contract terms, and another to release payment readiness. That does not mean every vendor requires executive review. It means the workflow separates risky duties at the right points.
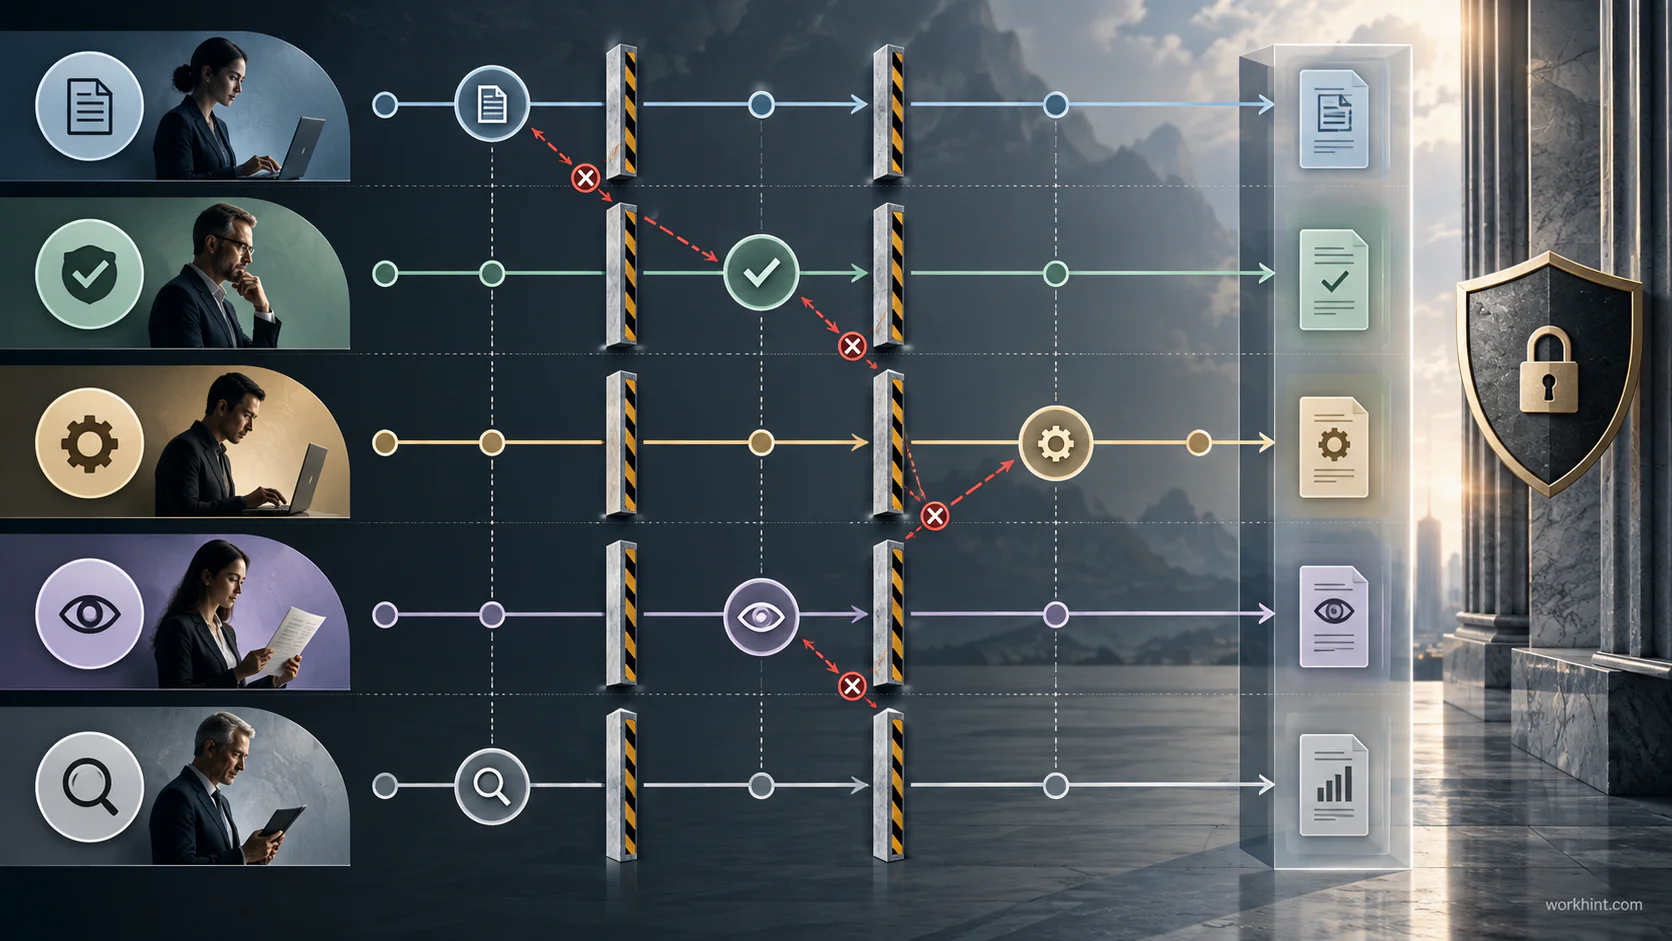
Segregation of duties matrix template
Use the matrix below as a starting point. Keep the first version focused on one process, such as procure-to-pay, vendor onboarding, system access, contract approval, or refunds.
| Field | What to define | Example |
|---|---|---|
| Process area | The workflow or business cycle covered | Vendor onboarding |
| Duty | The action being controlled | Create vendor record |
| Primary role | Who normally performs the duty | Procurement coordinator |
| Incompatible duty | The duty that should not be held by the same role | Approve bank details |
| Risk | What could go wrong if duties are combined | Fake vendor or redirected payment |
| Required control | Approval, review, restriction, or monitoring rule | Finance verifies payment details before activation |
| Compensating control | Fallback when full separation is not practical | Weekly controller review of new vendors |
| Evidence | The record that proves the control operated | Approval timestamp, verification note, change history |
How to build a segregation of duties matrix
1. Start with high-risk workflows. Do not try to map the entire company at once. Begin with workflows that involve payments, approvals, access, contracts, vendor records, payroll, refunds, financial entries, or sensitive data.
2. Break the workflow into duties. Separate the work into request, approve, execute, record, reconcile, review, and administer. Use plain language. “Create vendor,” “approve invoice,” “release payment,” and “review bank reconciliation” are clearer than broad phrases like “manage finance.”
3. Identify incompatible combinations. Look for pairs that would let one person complete and conceal a risky action. Common conflicts include creating a vendor and approving payment, submitting a purchase and approving it, provisioning access and approving access, or preparing and reviewing a reconciliation.
4. Assign role-based owners. Use roles, not only names. People change jobs; the control should survive the org change. Current assignees can be tracked separately inside the live workflow.
5. Define exceptions and compensating controls. Small teams may not be able to separate every duty perfectly. In that case, document the exception, assign a second review, require a periodic reconciliation, lower approval limits, add audit logging, or time-limit the access.
6. Turn the matrix into workflow rules. A spreadsheet is only the design layer. The control becomes real when the workflow enforces permissions, routes approvals, blocks self-approval, records evidence, and alerts owners when exceptions appear.
Where Workhint fits
Workhint helps teams turn a segregation of duties matrix into a working process, not a static control document. A team can use workflow automation software to define intake fields, role-based permissions, approval steps, exception paths, audit records, dashboards, and recurring reviews around the same duties listed in the matrix.
That matters because SoD controls often fail when they live outside the workflow. The policy says one person cannot approve their own request, but the form still routes to them. The matrix says finance must verify payment changes, but the evidence lives in email. A live work system connects the rule, role, action, and record in one place.
Common mistakes
- Starting with system permissions only. Access matters, but SoD should begin with the business process and the risk inside it.
- Making every workflow heavy. Separate duties where the risk justifies it. Do not add controls that create delay without reducing meaningful risk.
- Ignoring small-team realities. If perfect separation is impossible, document compensating controls instead of pretending the risk is gone.
- Leaving evidence undefined. A control without evidence is hard to prove later. Capture who acted, when, what changed, why, and which rule applied.
- Never reviewing conflicts. Roles, systems, vendors, and workflows change. Review the matrix after reorganizations, tool changes, new locations, or audit findings.
FAQ
What is a segregation of duties matrix?
It is a table that maps duties, roles, incompatible combinations, controls, exceptions, and evidence for a critical business process. It helps prevent one role from controlling an entire risky transaction.
What duties should be separated?
Common duties to separate include requesting, approving, executing, recording, reconciling, reviewing, and administering access. The exact separation depends on the workflow and risk.
Can small teams use segregation of duties?
Yes. Small teams may need compensating controls such as independent review, management signoff, audit logs, transaction sampling, lower approval limits, or periodic reconciliation.
Is segregation of duties only for finance?
No. It also applies to access management, vendor onboarding, contract approval, employee data changes, customer refunds, system configuration, compliance reviews, and operational exceptions.
Conclusion
A segregation of duties matrix gives operations teams a practical way to design controls into the workflow before risk becomes a cleanup problem. Start with one high-risk process, list the duties, identify incompatible combinations, assign role-based owners, define exceptions, and connect the matrix to workflow rules. The strongest version is not just a spreadsheet. It is an operating system that makes the right separation visible, enforceable, and reviewable.
Leave a Reply