

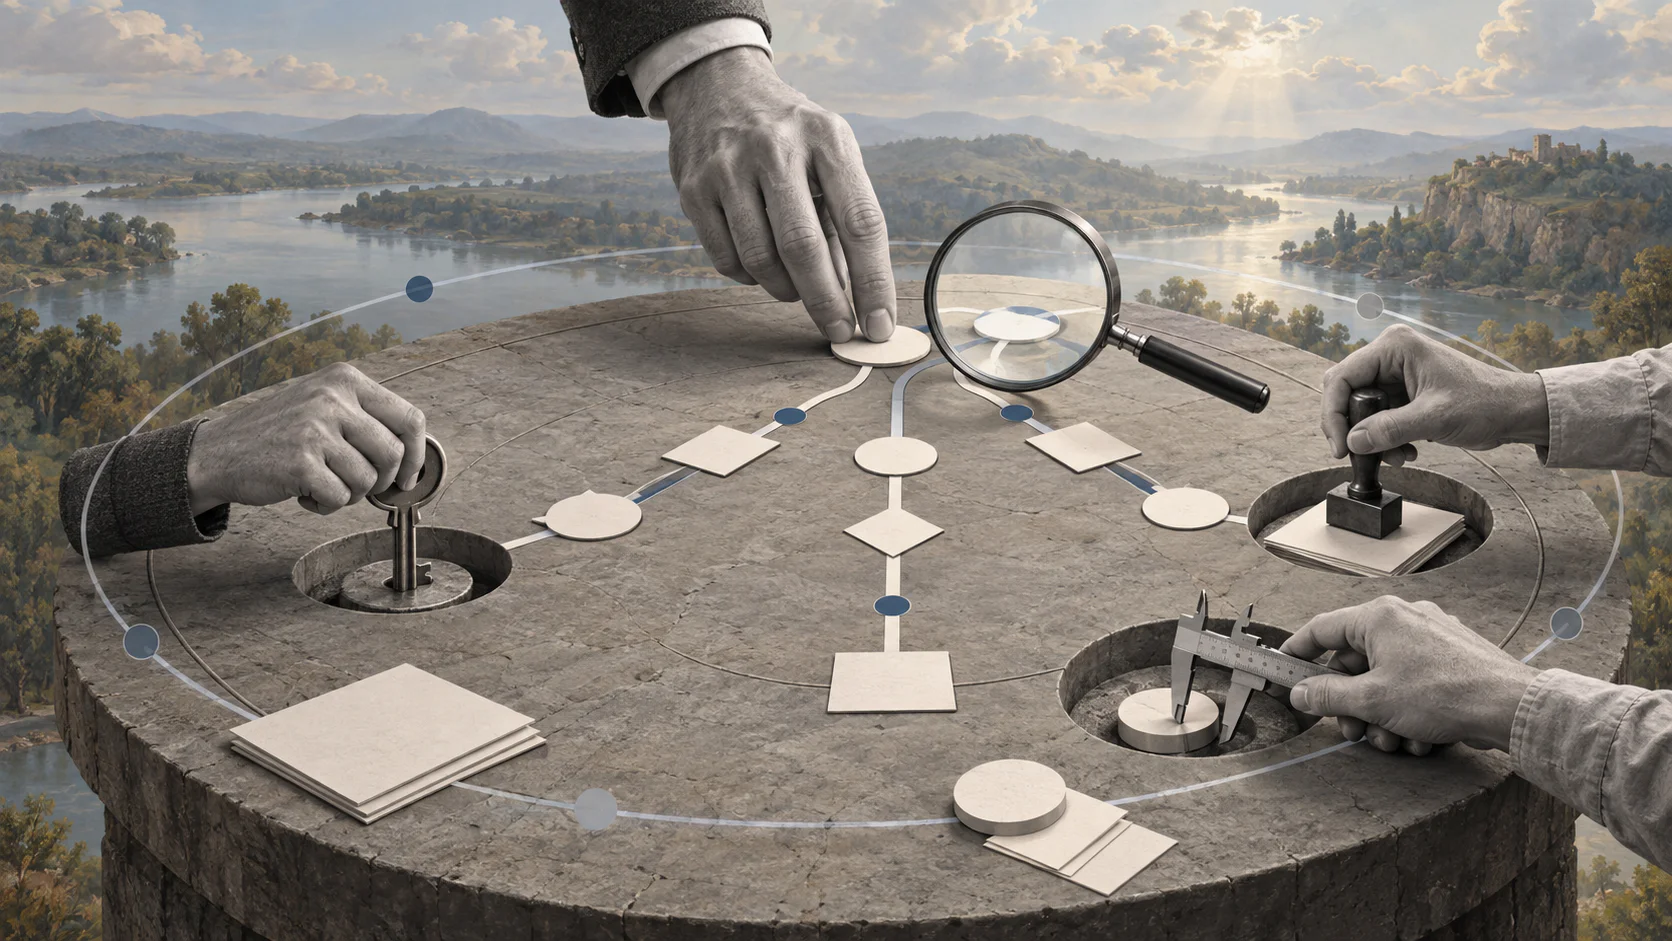
A planner can create the route, but reliable business automation depends on how each step is executed, checked, and recovered.
Planner executor architecture separates an AI agent’s strategy from its actions. A planner breaks a business goal into steps, while one or more executors use approved tools to complete those steps. This pattern can improve control and flexibility in complex work, but only when the plan, permissions, state, verification, and escalation rules are designed together.
Quick answer
A planner executor architecture uses one AI component to create or revise a task plan and separate executors to perform bounded actions. It is useful for multi-step work with changing conditions, such as resolving an invoice exception or onboarding a supplier. Use it only when a fixed workflow or single tool-using agent cannot meet the requirement reliably.
What’s in this article?
- When planner executor architecture is the right choice
- The components a production design needs
- A step-by-step implementation workflow
- Controls, metrics, and common failure modes
- A practical procurement example
What is planner executor architecture?
In a planner executor architecture, the planner interprets the goal, constraints, and available capabilities, then returns a structured sequence of work. The executor receives one bounded step at a time, invokes an approved model, API, database, or human task, and records the result. A controller decides whether to continue, replan, request review, or stop.
LangChain’s explanation of plan-and-execute agents describes the core split between a planner that generates a multi-step plan and executors that perform individual tasks. The pattern can reduce repeated use of a larger model, but it also creates new coordination and state-management requirements.
This is not automatically a multi-agent system. One service can implement both roles. Multiple agents make sense only when the work requires separate knowledge, tools, security boundaries, or parallel execution. Microsoft’s AI agent orchestration guidance recommends the lowest complexity that reliably meets the requirement because orchestration adds latency, cost, and failure modes.
When should a business use a planner executor agent?
Use this architecture when the path cannot be fully known in advance, but every action still needs boundaries. Strong candidates have several of these characteristics:
- The goal requires multiple tools, systems, or teams.
- Later steps depend on evidence returned by earlier steps.
- Exceptions can change the route.
- Some actions require human approval.
- Different steps need different permissions or models.
- The business needs a durable record of plans, actions, and outcomes.
Do not use it for deterministic work such as copying approved data between two systems or applying a fixed validation rule. A conventional workflow is cheaper, easier to test, and easier to audit. A single tool-using agent is also often enough when the task is short and the tool set is small.
What components should the architecture include?
| Component | Responsibility | Required control |
|---|---|---|
| Intake | Captures the goal, context, deadline, and requester | Schema validation and identity |
| Planner | Creates an ordered, structured plan | Allowed step types and step limit |
| Controller | Tracks state and selects the next action | Timeouts, budgets, and stop conditions |
| Executor | Runs one bounded step with approved tools | Least-privilege permissions |
| Verifier | Checks evidence and completion criteria | Independent rules or human review |
| Audit layer | Stores plan versions, actions, inputs, and outputs | Retention and access policy |
The plan should be machine-readable, not a paragraph. Each step needs an identifier, action type, required inputs, permitted tool, expected output, completion rule, retry policy, and escalation owner. This prevents the executor from inventing an unapproved route.
How do you implement a planner executor workflow?
- Define the business outcome. Specify what successful completion means in operational terms, such as an approved supplier record rather than “research the supplier.”
- Map the safe action set. List the APIs, searches, record updates, notifications, and human decisions an executor may use. Default to read-only access until a write is necessary.
- Create a plan schema. Require structured fields for dependencies, tool choice, evidence, risk level, and approval gates. Reject invalid plans before execution.
- Separate planning from authorization. A planner may propose a payment, access change, or contract action, but the controller must enforce policy and obtain approval.
- Persist state after every step. Record the plan version, input, tool response, verification result, cost, and next state so the workflow can resume safely.
- Verify before advancing. Use deterministic checks where possible. Use a second model or a human only when judgment is genuinely required.
- Set recovery rules. Define retry limits, alternative tools, replan triggers, human escalation, and terminal failure states.
- Test complete trajectories. Evaluate normal work, missing data, contradictory evidence, unavailable tools, permission failures, and attempts to exceed the action boundary.
OpenAI’s practical guide to building agents emphasizes clear instructions, well-defined tools, and guardrails. Business deployments should connect those controls to named owners, approval policies, and recovery paths.
Practical example: supplier onboarding
A procurement team receives a supplier request. The planner proposes steps to validate required fields, check sanctions and tax documents, classify risk, route security review when needed, create the supplier record, and notify the requester.
The executors do not share unrestricted access. The research executor can read approved sources. The document executor can extract fields but cannot approve them. The system-record executor can create a supplier only after the controller confirms every required approval. If a source is unavailable or two documents conflict, the controller pauses and assigns a human review instead of letting the planner improvise.
Measure this workflow by completed onboardings, exception rate, human-review rate, cycle time, cost per completed case, policy violations, and reopened cases. Model accuracy alone does not show whether the business process worked.
Common planner executor failure modes
- Overplanning: the agent creates unnecessary steps. Limit plan length and require a reason for each step.
- Plan drift: execution moves away from the original goal. Recheck the goal and constraints after material changes.
- Unsafe delegation: an executor receives broader access than its task requires. Bind permissions to step type and record.
- False completion: the agent reports success without evidence. Require verifiable completion criteria.
- Endless replanning: the system loops after repeated failures. Cap replans and escalate to a named owner.
- Lost state: a timeout causes duplicate or contradictory actions. Use durable state and idempotent writes.
Where Workhint fits
The model should plan and analyze; the operational system should control the work. Workhint can serve as that orchestration layer by turning an approved process into intake, roles, permissions, assignments, approvals, documents, schedules, records, notifications, and reporting. Teams can connect a planner or specialized AI executors while keeping human decisions and operational state inside a configurable workflow automation platform. This makes the agent part of a governed business process rather than an isolated automation.
FAQ
Is planner executor architecture the same as multi-agent architecture?
No. Planner and executor are roles. They can run inside one service or across multiple agents. Add separate agents only when specialization, security boundaries, or parallel work justify the added complexity.
Should the planner be allowed to call business systems?
Usually no. The planner should propose structured steps. A controller should validate policy, and a bounded executor should call the approved system with least-privilege access.
When should a planner replan?
Replan when evidence invalidates a dependency, a required tool is unavailable, a verifier rejects a result, or an approved business constraint changes. Do not replan merely because an action is slow.
How do teams evaluate the architecture?
Track successful business completion, evidence quality, policy violations, human interventions, cycle time, cost, retries, and recovery rate. Evaluate full trajectories, not only the planner’s text output.
Conclusion
Planner executor architecture is valuable when business work needs adaptive sequencing without uncontrolled autonomy. Start with a narrow outcome, structured plans, bounded executors, durable state, independent verification, and explicit human escalation. If a fixed workflow can solve the problem, keep the simpler design. If planning is necessary, make operational control part of the architecture from the beginning.
Leave a Reply