

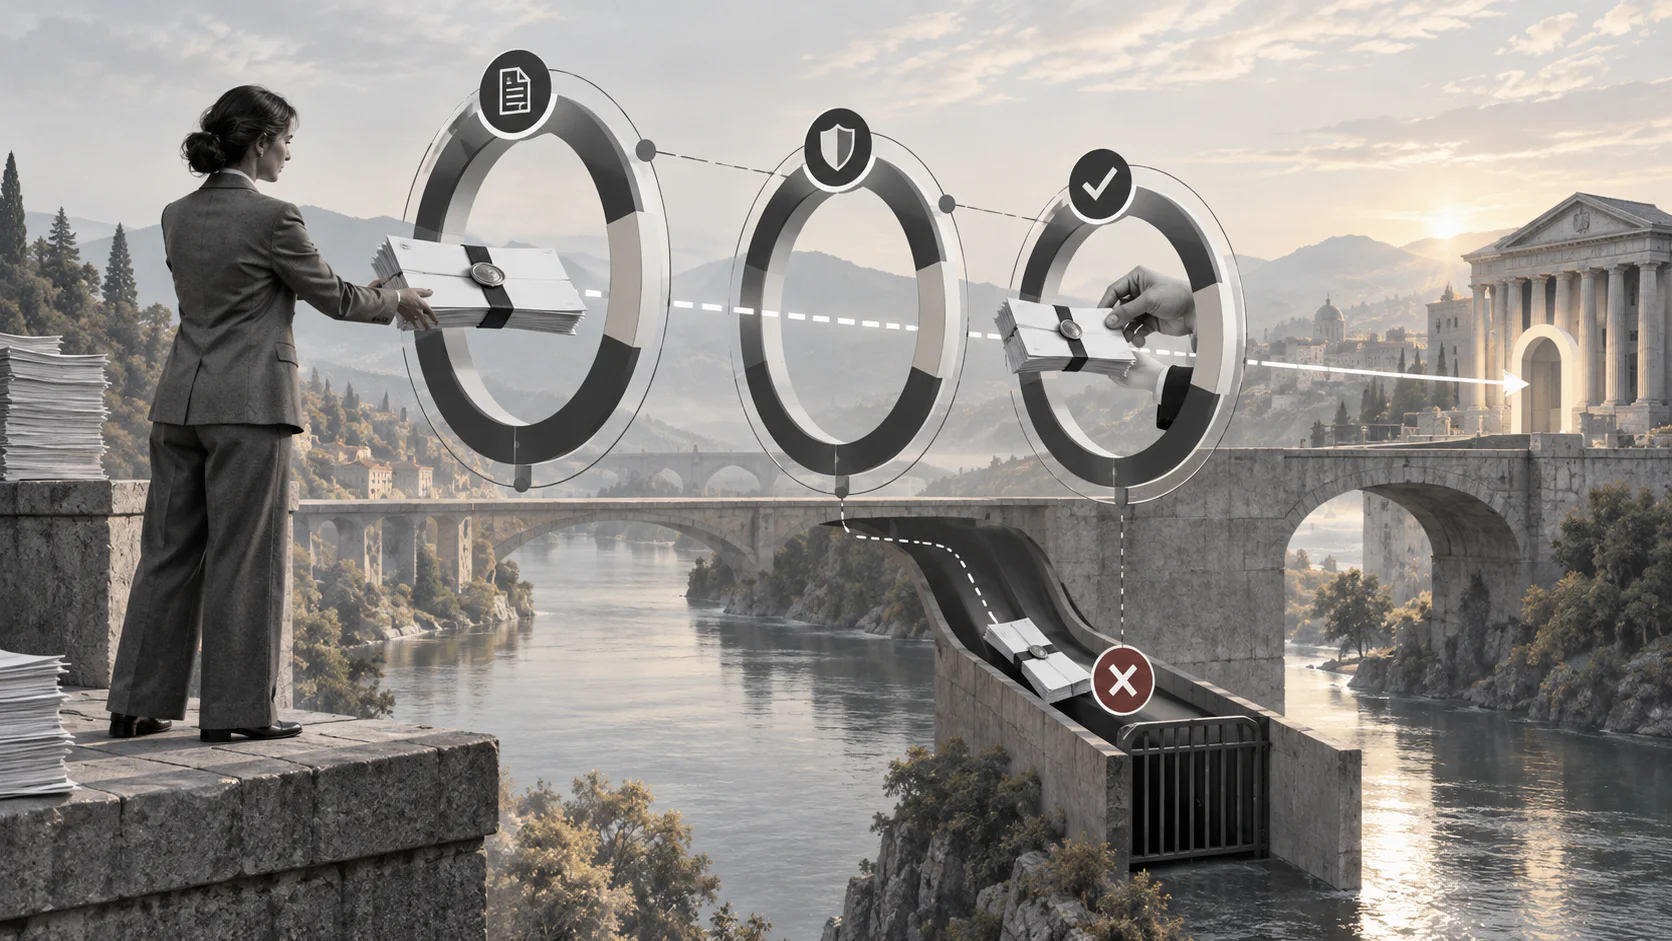
A clean payment run can still fail if the file reaching the bank is changed, duplicated, or approved by the wrong person.
Bank payment file controls protect the point where approved obligations become executable bank instructions. The control design must cover more than file creation: it should validate source records, restrict access, separate preparation from approval, protect transmission, confirm bank acceptance, and reconcile every released payment.
Quick answer
Strong bank payment file controls use an approved and locked payment batch, independent maker-checker approval, verified beneficiary changes, role-based access, file integrity checks, secure bank transmission, duplicate-file prevention, bank acceptance review, and prompt reconciliation. Every file should have a unique batch ID, documented totals, named owners, and an audit trail from approved invoice to settled transaction.
What’s in this article?
- What a bank payment file contains
- Which risks exist before and after transmission
- A control matrix for each stage
- How to handle rejects, changes, and emergency payments
What is a bank payment file?
A bank payment file is a structured set of payment instructions uploaded or transmitted to a bank. It may contain supplier, contractor, payroll, refund, or intercompany payments. Common formats include ACH files, bank-specific templates, CSV files, and XML messages based on standards such as ISO 20022.
The ISO 20022 message catalogue includes payment-initiation messages designed to carry structured payment information. Regardless of format, the file normally contains beneficiary details, amount, currency, requested execution date, reference data, and the account that will fund the payment.
The risk is concentrated: a single file may release hundreds or thousands of payments. A wrong account number, repeated batch, unauthorized edit, or compromised approval can create losses faster than invoice-by-invoice processing.
Where do payment file risks enter the process?
Risk can enter before the file exists. Fraudulent vendor bank changes, duplicate invoices, incorrect currencies, or unapproved items may already be present in the source batch. Risk can also appear during file generation, manual formatting, desktop storage, email transfer, portal upload, approval, or bank processing.
Business email compromise is especially relevant when attackers impersonate executives or suppliers and request payment changes. The FBI’s Internet Crime Report continues to identify business email compromise as a major source of reported losses. Finance teams should therefore verify sensitive beneficiary changes through a trusted channel that does not rely on the change request itself.
What controls belong at each payment file stage?
| Stage | Primary risk | Control | Evidence |
|---|---|---|---|
| Source selection | Unapproved or duplicate items | Include only approved, due, unblocked obligations | Locked batch and approval record |
| Beneficiary data | Fraudulent bank change | Out-of-band verification and change cooling period | Verification log |
| File generation | Wrong totals or format | System-generated file, control totals, unique batch ID | File summary and hash |
| Approval | Self-approval or excess authority | Maker-checker separation and amount thresholds | Timestamped approval trail |
| Transmission | Interception or substitution | Bank API, secure host-to-host channel, or controlled portal upload | Transmission receipt |
| Bank response | Silent rejects or duplicates | Review acceptance, rejection, and duplicate warnings | Bank acknowledgement |
| Settlement | Unrecorded failure or wrong posting | Reconcile settled payments to file and ledger | Reconciliation sign-off |
How should the payment file approval workflow work?
- Freeze the source batch. Once preparation starts, prevent silent additions or edits. Any change should create a new version and require reapproval.
- Compare control totals. The preparer records payment count, total value, currency totals, funding account, and execution date. The generated file must match.
- Run exception checks. Flag new beneficiaries, bank-detail changes, round-dollar amounts, payments above thresholds, unusual countries, and duplicates.
- Require independent approval. The approver must see the batch summary and exceptions, not merely an “approve” button. High-value or sensitive batches may need a second approver.
- Transmit through an authorized channel. Avoid sending executable files through ordinary email or unmanaged file sharing.
- Confirm bank acceptance. An upload confirmation is not settlement. Capture accepted, rejected, held, and partially processed instructions.
- Reconcile and close. Match bank results to the batch, update payment status, investigate exceptions, and retain evidence.
For ACH activity, Nacha’s data security requirements highlight security expectations around protected ACH account information. The broader principle applies across rails: protect account information, limit unnecessary access, and document control performance.
How do you protect the file itself?
Store payment files only in controlled locations with least-privilege access and short retention periods. Disable shared credentials, require strong authentication, and log downloads, edits, approvals, and transmissions. A cryptographic hash can help confirm that the approved file is the file transmitted, while a unique batch identifier helps block accidental re-uploads.
Controls should follow the organization’s wider cybersecurity program. The NIST Cybersecurity Framework provides a useful structure for identifying risks, protecting systems, detecting anomalies, responding to incidents, and recovering operations.
What should happen when a file is rejected or changed?
Never edit an approved file manually and upload it again under the same approval. A rejected file should enter a controlled exception process: record the bank reason, correct the source record, regenerate the batch, rerun validation, and obtain fresh approval. The same rule should apply when a funding account, execution date, beneficiary, currency, or amount changes.
Emergency payments need a defined path, not a control bypass. Set narrower authority, require documented business justification, verify beneficiary data, and complete next-day independent review.
Where does Workhint fit?
The ERP and bank remain the systems of record for obligations and settlement. Workhint can coordinate the surrounding control process: route batches by value and entity, enforce maker-checker assignments, collect beneficiary-change evidence, track exceptions, escalate delayed approvals, and preserve an operational audit trail. With workflow automation software, teams can make the control sequence repeatable across entities without relying on email chains and manual reminders.
Frequently asked questions
Should payment files ever be emailed?
Executable payment files should use an approved secure channel. Ordinary email creates avoidable access, substitution, forwarding, and retention risks.
What is maker-checker control?
One authorized person prepares the batch or file, while a different authorized person independently reviews and approves it. The preparer cannot approve their own work.
Does bank approval replace internal approval?
No. Bank portal approval controls release at the bank, but internal approval should establish that the underlying obligations, beneficiaries, amounts, and authority are valid.
How long should payment file evidence be retained?
Follow the company’s legal, tax, audit, banking, and records-retention requirements. Retain the evidence needed to trace each payment from obligation through approval, transmission, settlement, and ledger posting.
Conclusion
Bank payment file controls should create one traceable chain from approved obligation to reconciled settlement. Lock the source batch, verify sensitive changes, separate duties, protect file integrity, confirm bank responses, and reapprove every material change. That discipline reduces fraud and error without slowing well-designed payment operations.
Leave a Reply