

Use this checklist to catch unclear vendor terms before pricing, access, data, or renewal risk turns into an operating problem.
A vendor contract review checklist gives procurement, finance, legal, security, and operations a shared way to review a supplier agreement before anyone signs. The point is not to turn every business owner into a lawyer. The point is to make sure the right people check the right terms, document exceptions, and approve risk with their eyes open.
Quick answer
A vendor contract review checklist should cover scope, deliverables, pricing, payment terms, service levels, confidentiality, data protection, intellectual property, liability, indemnification, insurance, termination, auto-renewal, audit rights, compliance, and approval sign-off. Each item should have an owner, evidence reviewed, risk decision, and follow-up action before the contract is signed.
What’s included
- A practical checklist for reviewing vendor contracts before signature.
- A risk table procurement, finance, legal, security, and operations can share.
- Common red flags to escalate before work starts.
- A simple approval record for documenting who reviewed what.
How to use this checklist
Use the checklist after the vendor has been selected but before the agreement is signed. For low-risk purchases, one business owner and one finance or procurement reviewer may be enough. For higher-risk vendors, add legal, security, privacy, compliance, and an executive approver when the contract touches sensitive data, critical operations, regulated work, unusual pricing, or material financial exposure.
This is general business guidance, not legal advice. Contract requirements depend on jurisdiction, industry, risk level, and the value of the relationship. Use this checklist to structure review, then involve qualified counsel for high-value, complex, regulated, or heavily negotiated agreements.
Vendor contract review checklist before signing
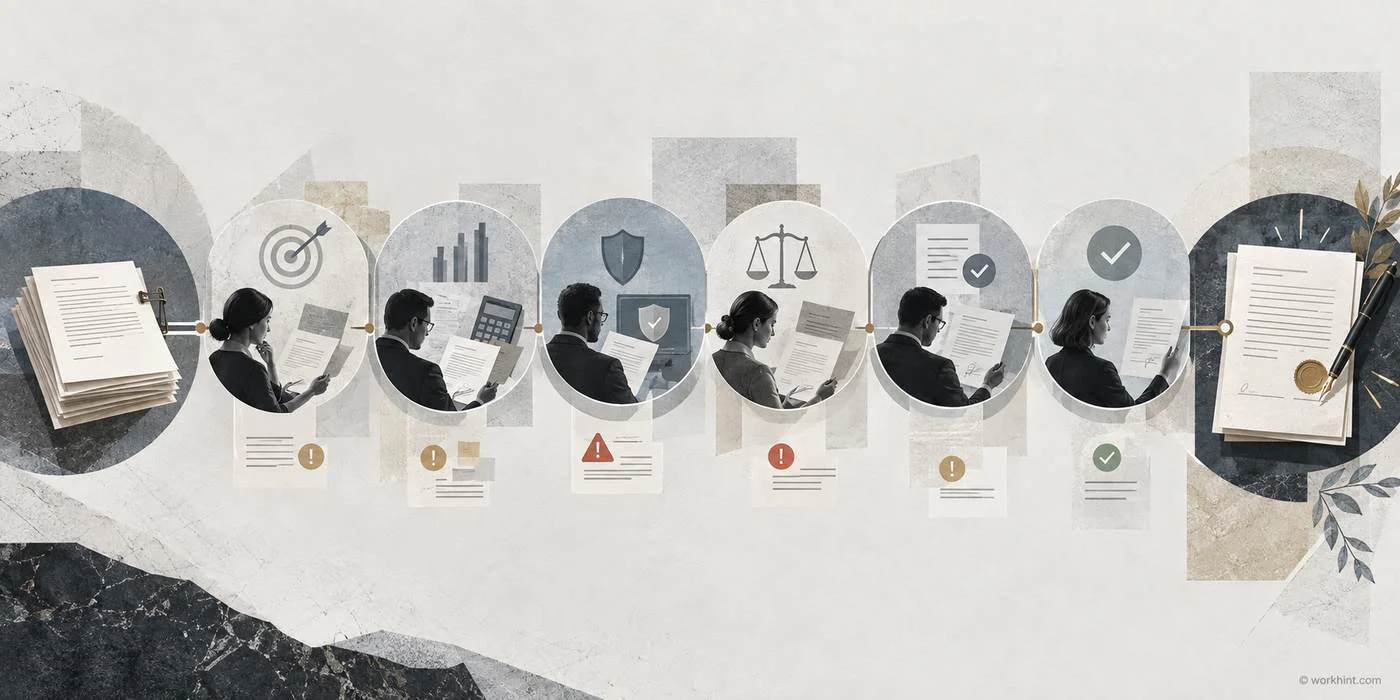
| Review area | Question to answer | Typical owner | Evidence to keep |
|---|---|---|---|
| Scope and deliverables | Does the contract clearly state what the vendor will provide, what is out of scope, and how completion is measured? | Business owner | Final scope, SOW, deliverable table, acceptance criteria |
| Pricing and payment | Are fees, taxes, expenses, price increases, invoice timing, and payment triggers clear? | Finance | Pricing schedule, invoice rules, budget approval |
| Service levels | Are response times, uptime, remedies, credits, and escalation paths specific enough to enforce? | Operations | SLA, support terms, escalation contacts |
| Data and security | Will the vendor access systems, customer information, employee data, payment data, or confidential records? | Security or privacy | DPA, security review, access notes, retention terms |
| Liability and indemnity | Are liability caps, exclusions, indemnities, and insurance requirements acceptable for the risk? | Legal | Marked contract, insurance certificate, legal notes |
| Term and renewal | Can the company exit, avoid unwanted auto-renewal, and recover data or materials at termination? | Procurement | Renewal calendar, notice deadline, termination clause |
| Compliance and screening | Does the vendor need licenses, sanctions screening, regulatory commitments, or audit cooperation? | Compliance | Screening result, license evidence, audit clause |
| Approval sign-off | Has every required reviewer approved, rejected, or accepted an exception with a reason? | Procurement | Approval record, exception log, final signed copy |
What to check in the scope and deliverables
Most contract problems start with vague work. The contract should name the service, deliverables, timeline, acceptance criteria, business owner, dependencies, and exclusions. Thomson Reuters notes that a statement of work commonly covers roles, responsibilities, deliverables, schedule, service expectations, and acceptance criteria. Even when the vendor contract is not a formal SOW, those same details help prevent disputes.
Look for phrases that sound useful but cannot be enforced, such as “support as needed,” “reasonable efforts,” or “ongoing assistance” without limits. Replace vague language with deliverables, dates, formats, service levels, and named approval owners.
What to check in pricing and payment terms
Finance should confirm total cost, recurring fees, implementation fees, reimbursable expenses, taxes, late fees, currency, invoice submission rules, payment timing, and price increase rights. Watch for minimum commitments, usage overages, automatic uplifts, bundled services, and cancellation fees that make the contract more expensive than the headline price.
If payment depends on milestones, the milestone should connect to acceptance criteria. If payment is recurring, the contract should say when billing begins, what happens during suspension, and how credits or refunds are handled when service fails.
What to check for data, security, and compliance
Any vendor that handles sensitive data, customer records, payment information, employee data, or system access deserves a deeper review. The FTC Safeguards Rule guidance tells covered businesses to oversee service providers that handle customer information and take steps to ensure those providers safeguard it. The same operating principle is useful more broadly: know what data the vendor touches, what controls apply, and what happens when the relationship ends.
For certain vendors, procurement or compliance may also need sanctions or restricted-party screening. The U.S. Treasury provides OFAC sanctions list resources that teams can use as part of a documented screening process when relevant to the relationship, payment route, or policy.
Common red flags
- The vendor can change pricing or scope without written approval.
- The contract renews automatically unless notice is given far in advance.
- Acceptance is unclear, so payment can be due before work is usable.
- The vendor disclaims too much responsibility for data, downtime, or security incidents.
- Termination rights exist on paper but require long notice, large fees, or vendor-controlled data return.
- Insurance, confidentiality, audit rights, or subcontractor terms are missing for a high-risk vendor.
- No internal owner is accountable for monitoring renewal dates, service performance, or contract obligations.
Example approval record
| Reviewer | Area reviewed | Decision | Open condition |
|---|---|---|---|
| Operations | Scope, timeline, service levels | Approve with edits | Add named escalation contact and response time |
| Finance | Pricing, invoicing, budget | Approve | None |
| Security | System access and data protection | Conditional approval | DPA required before access is granted |
| Legal | Liability, termination, governing terms | Approve with exception | Liability cap accepted by VP Operations |
Where Workhint fits
A checklist is useful, but vendor contracts break down when the checklist lives in a document and the work happens somewhere else. Workhint helps teams turn vendor review into a live workflow: intake captures the vendor, contract value, data access, owner, and start date; routing sends the right sections to finance, legal, security, compliance, and operations; approvals and exceptions are recorded; renewal dates and follow-ups become assigned work.
For teams managing many suppliers, vendor management software can connect review, onboarding, documents, approvals, performance tracking, renewal reminders, and audit evidence in one operating system instead of leaving contract risk scattered across email and spreadsheets.
FAQ
What is a vendor contract review checklist?
A vendor contract review checklist is a structured list of contract areas to check before signing a supplier agreement. It helps teams review scope, price, payment, service levels, data protection, liability, termination, compliance, and approvals consistently.
Who should review a vendor contract?
At minimum, the business owner and procurement or finance should review the contract. Add legal for contract risk, security or privacy for data and system access, compliance for regulated work, and executive approval for high-value or high-risk vendors.
What is the biggest vendor contract red flag?
The biggest red flag is unclear responsibility. If the contract does not define what the vendor will deliver, how success is accepted, what happens when service fails, and who owns follow-up, the business may have little leverage after signing.
Should every vendor contract go to legal?
Not always. Low-value, standard purchases may follow a lighter review path. Legal review is more important for high-value contracts, sensitive data, custom deliverables, unusual liability terms, regulated work, long commitments, or vendor terms that cannot be easily changed later.
Conclusion
A vendor contract review checklist works best when it produces a decision, not just a marked-up document. Before signing, confirm the scope is enforceable, the pricing is understood, the risk is assigned, the right reviewers have approved, and every exception has an owner. That is what turns contract review from paperwork into operational control.
Leave a Reply